

Employee Applicant Privacy Notice
Who we are:
Shape a brighter financial future with us.
Together with our members, we’re changing the way people think about and interact with personal finance.
We’re a next-generation financial services company and national bank using innovative, mobile-first technology to help our millions of members reach their goals. The industry is going through an unprecedented transformation, and we’re at the forefront. We’re proud to come to work every day knowing that what we do has a direct impact on people’s lives, with our core values guiding us every step of the way. Join us to invest in yourself, your career, and the financial world.
The role:
As a Senior Staff Incident Response Engineer on the Cyber Defense team, you will serve as the principal technical authority and subject matter expert for incident response within SoFi’s Security Operations Center (SOC). You will lead investigations and mitigation actions against threats targeting crypto and digital asset platforms, while securing our core enterprise and cloud infrastructure (AWS/GCP, applications, identity, and endpoints).
This position sits within Incident Response (IR) in SoFi’s Cyber Defense organization. In partnership with our Cyber Incident Commander, you will handle high-severity incidents, architect containment workflows, and lead technical forensics across distributed systems. Pairing specialized digital asset threat knowledge with an engineering skill set, you will perform forensic triage, build automated investigation tools, and translate findings into hardened detection mechanisms and playbooks across the enterprise.
What you’ll do:
- Serve as the SOC’s subject matter expert for digital asset and cryptocurrency security, investigating and neutralizing threats directed at digital asset platforms and services.
- Apply blockchain investigation methods, forensic telemetry, and analytical tooling to execute scoping, containment, and recovery operations.
- Investigate and resolve security alerts and incidents across digital asset, cloud, application, identity, and endpoint environments, driving issues from initial triage to root cause and remediation.
- Perform forensic triage and deep data study, including cloud and application log review, endpoint artifact inspection, evidence preservation, and timeline reconstruction.
- Write clean, maintainable code (Python, Go, or SQL) to test large datasets, correlate telemetry across disparate log sources, and automate evidence collection and enrichment workflows.
- Partner cross-functionally with Detection Engineering, Application Security, and Core Infrastructure teams to construct and tune threat detections, address logging gaps, and track systemic remediations to completion.
- Partner with SOC analysts and the Cyber Incident Commander on incident operations, providing technical direction on complex investigations and high-severity incidents.
- Develop and maintain crypto-specific and cloud-specific incident response runbooks and response procedures.
- Document investigations thoroughly and deliver technical findings and post-incident reviews to technical and executive stakeholders.
- Lead technical simulations and tabletop exercises encompassing digital asset and smart contract failure modes.
- Evaluate and engineer automation tooling, including SOAR and AI-assisted investigation workflows, to increase response efficiency, consistency, and coverage.
- Mentor engineers, conduct peer reviews, and elevate the technical standards of the SOC through threat education and reusable software tooling.
What you’ll need:
- Education & Minimum Experience Requirements: Bachelor’s degree + 4+ years of relevant experience OR Master’s degree + 3+ years of relevant experience.
- 8+ years of total experience in incident response, security operations, or related security engineering functions within enterprise environments.
- Proven hands-on experience investigating security incidents involving cryptocurrency, blockchain protocols, or digital asset platforms.
- Solid understanding of blockchain fundamentals, smart contract interaction models, and digital asset attack vectors.
- Demonstrated experience utilizing blockchain analytics and forensic tooling.
- Hands-on experience leading investigations across cloud (AWS, GCP, or Azure), containerized, application, endpoint, network, and identity environments.
- Solid engineering background with proficiency in at least one modern language (such as Python or Go) and SQL, with the ability to build automated investigation tools and query high-volume datasets.
- Solid grounding in digital forensics fundamentals, including chain of custody, evidence handling, memory inspection, and disk/log triage.
- Comprehensive understanding of the incident response lifecycle and industry frameworks (such as NIST SP 800-61 and MITRE ATT&CK).
- Hands-on knowledge of enterprise security platforms including SIEM, EDR, identity providers, and cloud security posture tooling.
- Solid understanding of operating system internals (Linux, macOS, Windows) and enterprise networking fundamentals.
- Proven ability to work cross-functionally, align partners, and maintain composure while managing high-pressure incidents.
- Clear written and verbal communication skills, including the ability to communicate technical findings to varied audiences.
Nice to have:
- Experience with commercial blockchain intelligence platforms
- Hands-on experience in smart contract auditing, vulnerability assessments, or blockchain security engineering.
- Track record of writing and tuning custom detections for cryptocurrency theft, wallet drainers, or financial fraud patterns.
- Experience operating within financial services, fintech, or regulated enterprise environments.
- Working knowledge of Kubernetes, container runtimes, and cloud-native security controls.
- Practical experience implementing SOAR automation playbooks or AI-assisted triage tooling.
- Familiarity with regulatory reporting obligations, breach disclosure requirements, and compliance standards governing digital assets.
- Industry security certifications (e.g., GCFA, GCFE, GNFA, GCIH) or dedicated blockchain security credentials.
SoFi San Francisco, California, USA Office
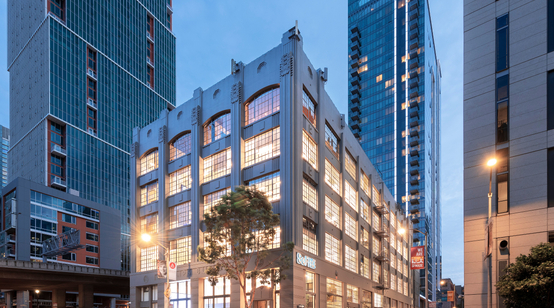
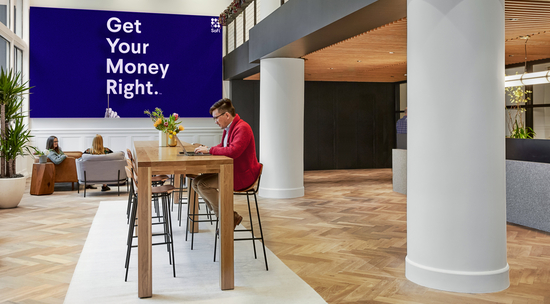
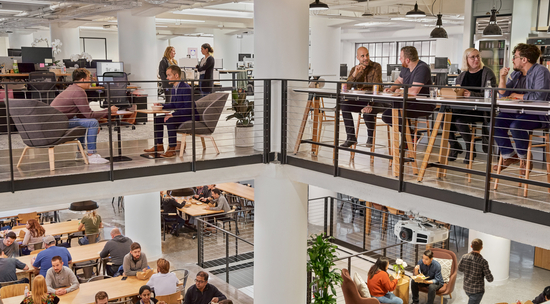
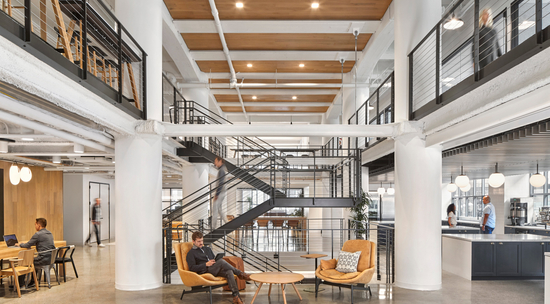
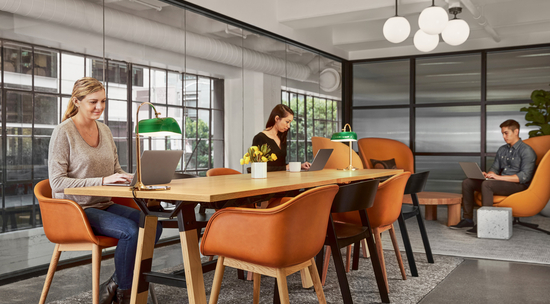
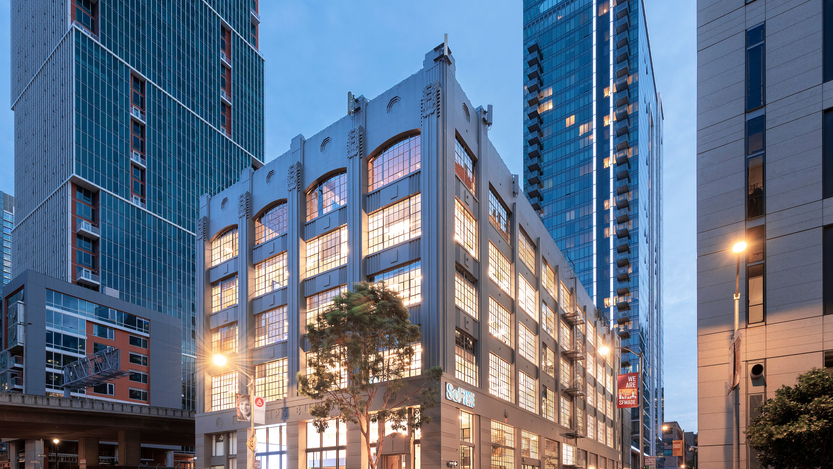
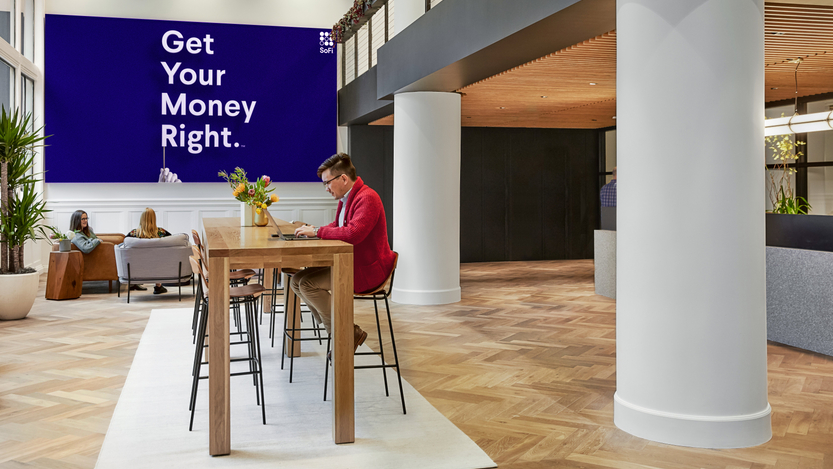
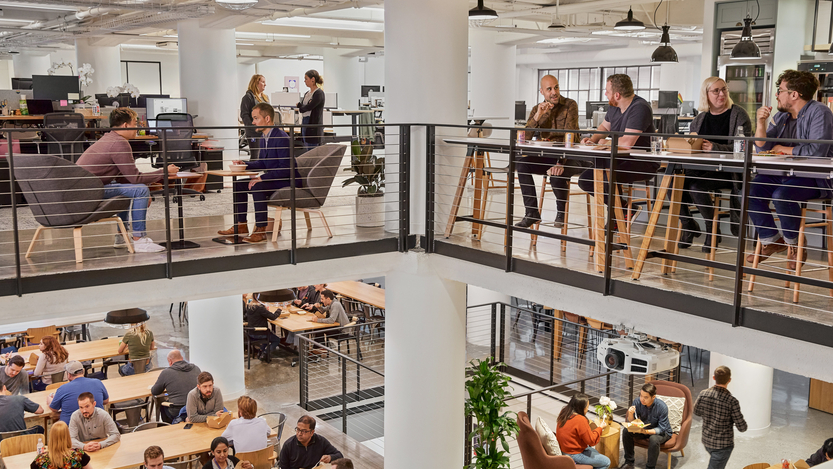
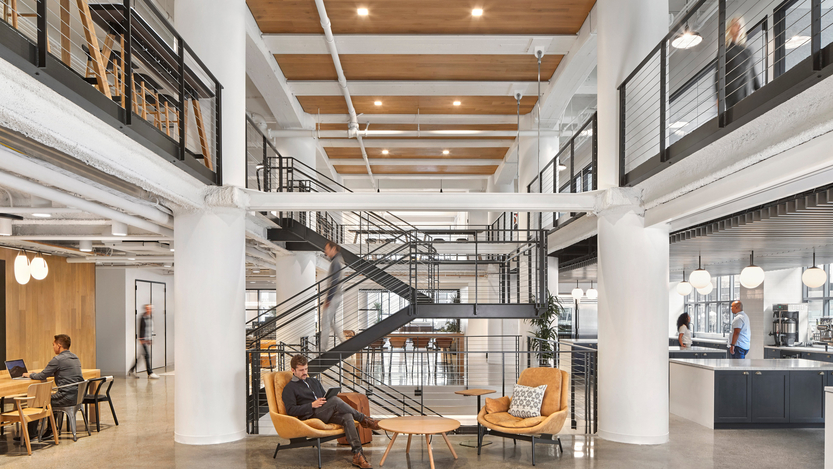
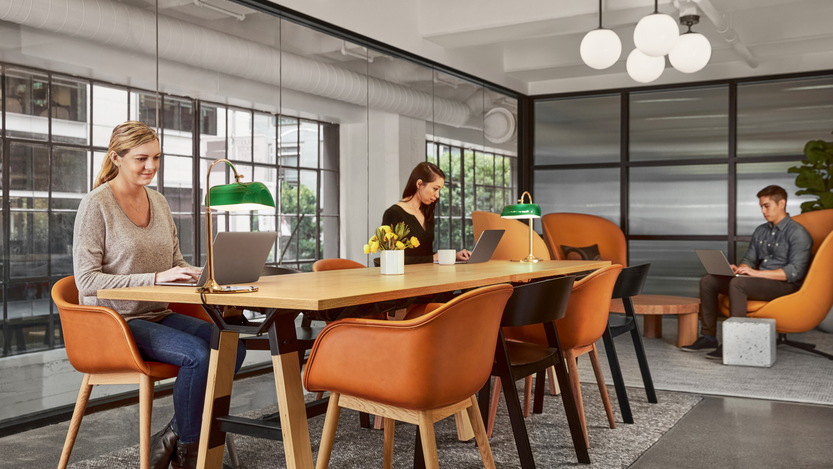
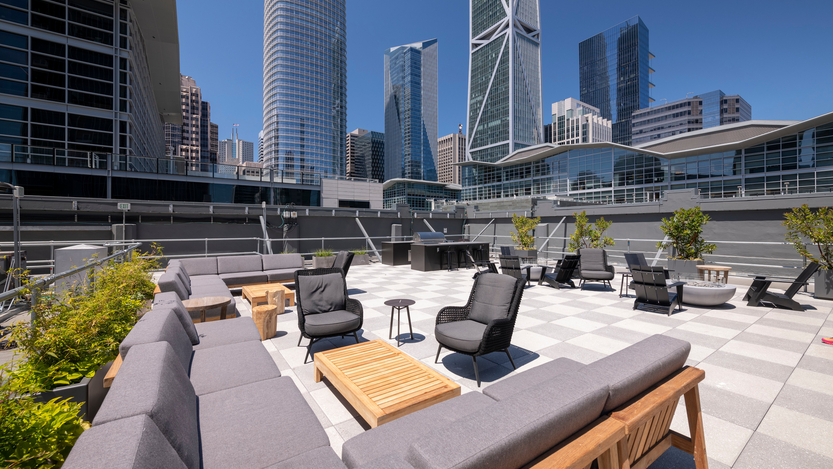
Our new headquarters opened in 2019. The office provides an open work environment, an all-hands area, a café, library, coffee points on every floor, and executive conference rooms. The game room and roof-top lounge area provide space to take a break and look at the incredible downtown view.
Similar Jobs at SoFi
What you need to know about the San Francisco Tech Scene
Key Facts About San Francisco Tech
- Number of Tech Workers: 365,500; 13.9% of overall workforce (2024 CompTIA survey)
- Major Tech Employers: Google, Apple, Salesforce, Meta
- Key Industries: Artificial intelligence, cloud computing, fintech, consumer technology, software
- Funding Landscape: $50.5 billion in venture capital funding in 2024 (Pitchbook)
- Notable Investors: Sequoia Capital, Andreessen Horowitz, Bessemer Venture Partners, Greylock Partners, Khosla Ventures, Kleiner Perkins
- Research Centers and Universities: Stanford University; University of California, Berkeley; University of San Francisco; Santa Clara University; Ames Research Center; Center for AI Safety; California Institute for Regenerative Medicine
